


The PeopleDAO Community Treasury on Safe has fallen prey to a social engineering attack during its monthly reward payout on March 6th, losing 76 ETH (~$120,000) in the process.
1/10
— PeopleDAO (📜, 🤝) (@The_PeopleDAO) March 11, 2023
Bad news:
PeopleDAO Community Treasury on @safe has recently been exploited of 76 ETH (~$120,000) via social engineering during monthly reward payout on March 6th.
This expoloit is not related to $PEOPLE token contract.
Details below:
According to PeopleDAO, the hack was not related to the $PEOPLE token contract. PeopleDAO collects monthly contributor reward information through a Google Form, and the accounting lead mistakenly shared an editable link on a public Discord channel, which the hacker gained access to. The hacker then inserted a 76 ETH payment to their own address in the sheet, and made it invisible. The team leads did not notice the malicious transfer during recheck. The CSV with the injected data was then downloaded and submitted to the CSV Airdrop tool in Safe to distribute rewards. As the transaction contained 80 transfers, 6 out of 9 multisig signers did not notice the fraudulent transfer, signed and executed the transaction, thereby sending 76 ETH to the hacker's address. The exploited fund was deposited into two exchanges, HitBTC and Binance.
PeopleDAO has reported the fraud case to the FBI and the FTC and is working with various organizations to find the hacker and recover the funds. They have also offered a 10% white hat bounty to the hacker if they return the stolen fund in the next 48 hours.
Full thread:
1/10
Bad news:
PeopleDAO Community Treasury on @safe has recently been exploited of 76 ETH (~$120,000) via social engineering during monthly reward payout on March 6th.
This expoloit is not related to $PEOPLE token contract.
Details below:
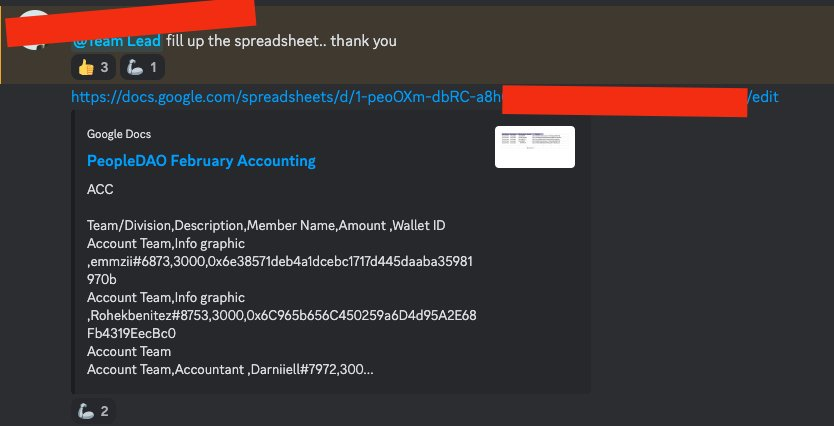
2/10 PeopleDAO collects monthly contributor reward information via Google Form. The accounting lead mistakenly shared a link with edit access in a public channel in discord. The hacker gained edit role via the link.
3/10 After gaining the access, the hacker inserted a 76 ETH payment to himself in the sheet, and set it invisible (the missing 80th row below).
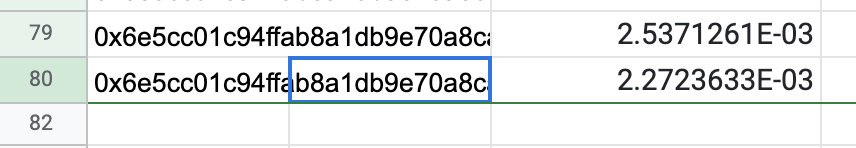
4/10 Because the malicious is hidden, team leads did not find it during recheck.
Then the csv with the insertef data was downloaded, and submitted to CSV Airdrop tool in Safe to distribute the reward.
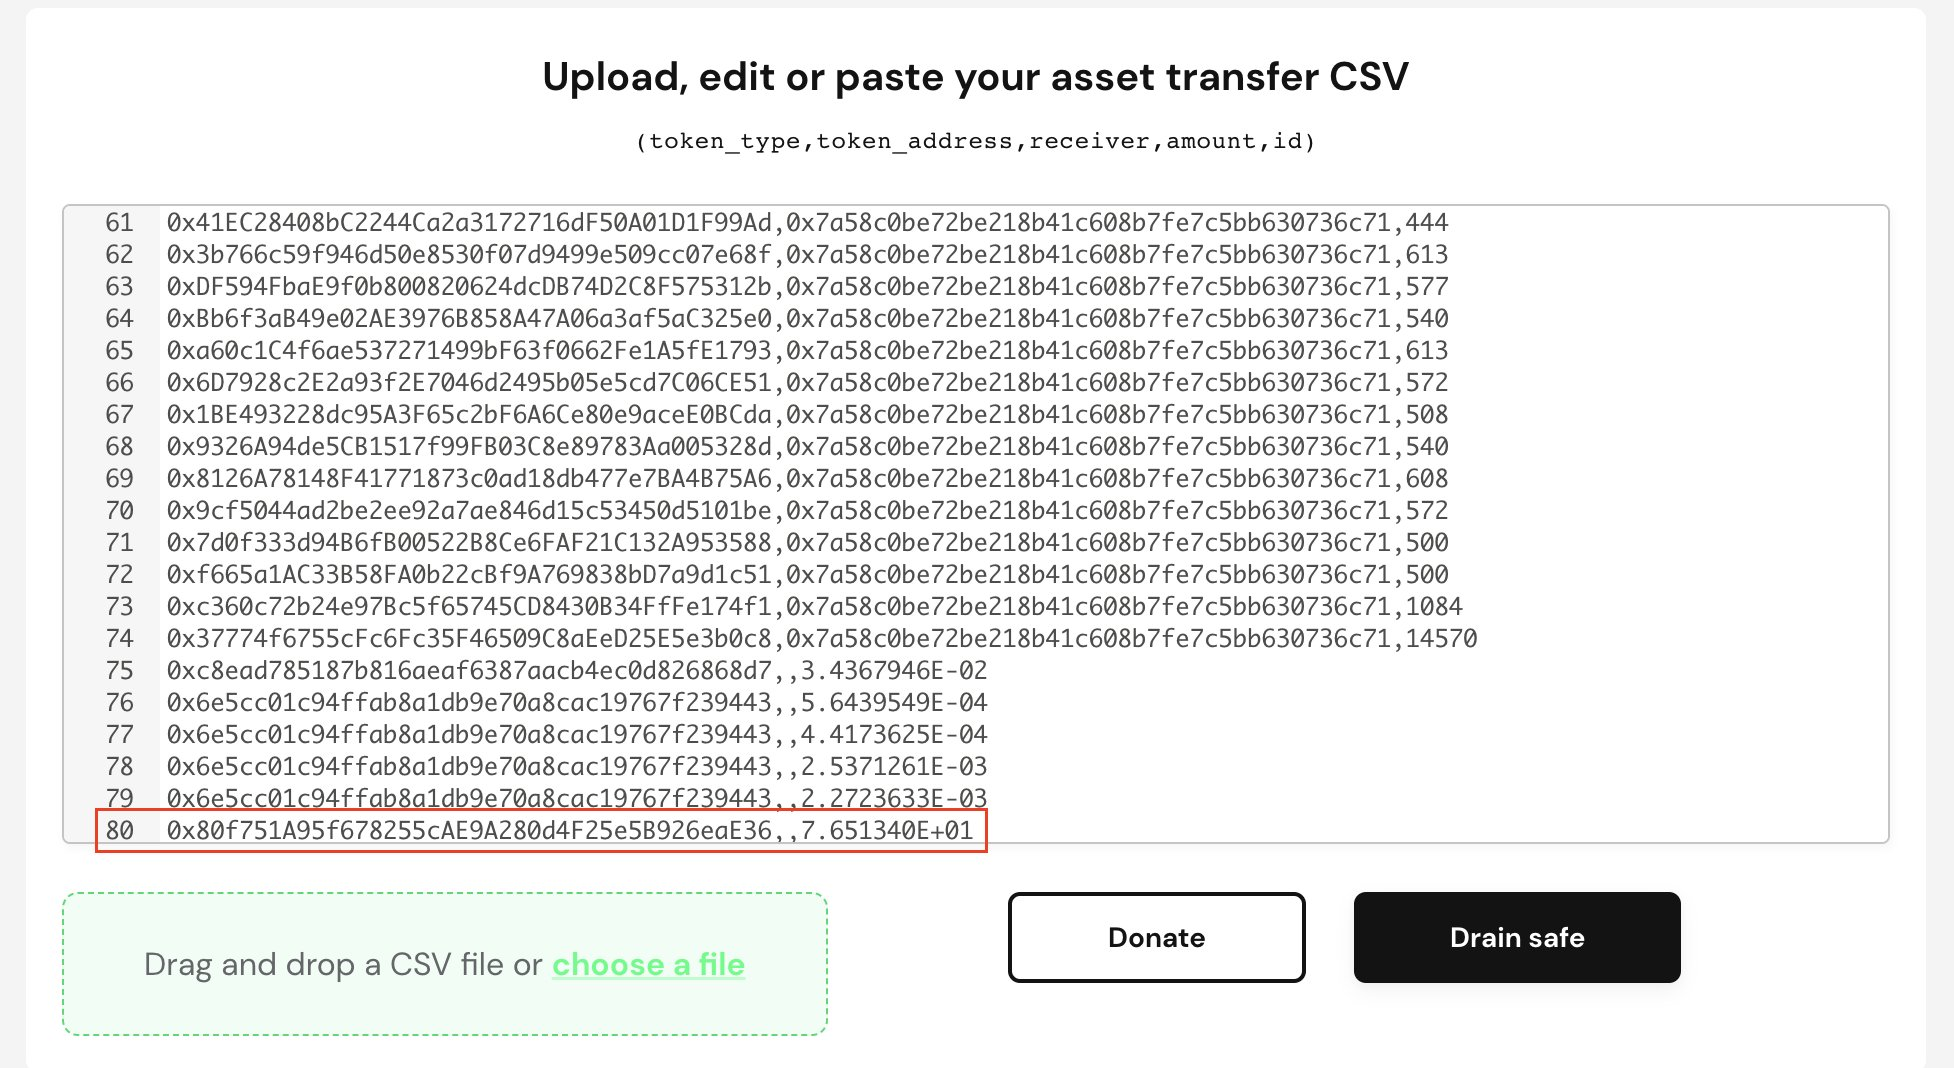
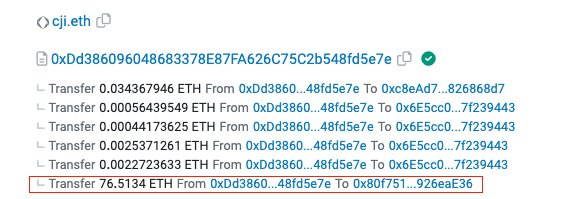
5/10 Because there are 80 transfers in the tx, 6 out of 9 multisig signers did not notice the malicious transfer, signed and executed the tx, sending 76 ETH to the hacker's address. Txhash: https://etherscan.io/tx/0x4bd2f6981b6b3005da8730bc14bfbbf36bd9faab6b5976012830c6235ea0afcf6… Hacker address: 0x80f751a95f678255cae9a280d4f25e5b926eae366
6/10 Working with @SlowMist_Team and @zachxbt , we find the exploited fund was then deposited into two exchanges, HitBTC @hitbtc and Binance @binance@cz_binance . We contacted them immediately after the loss.
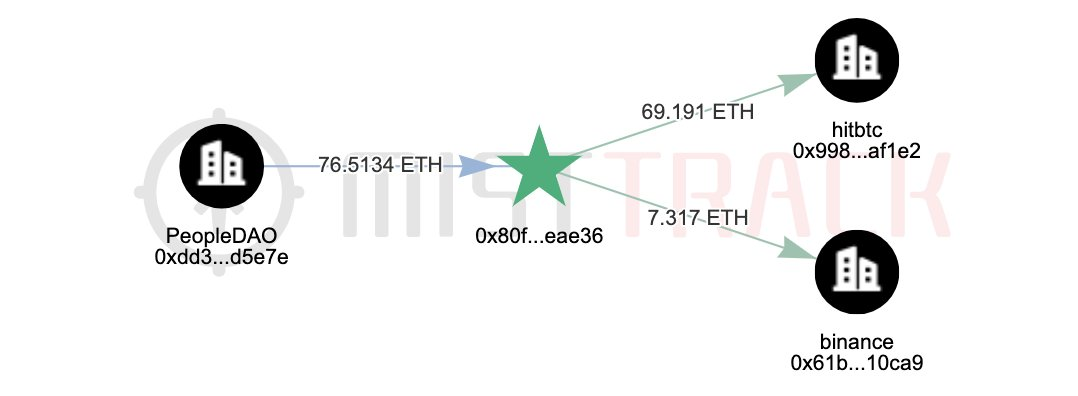
7/10 Moreover, we have reported the fraud case to FBI @FBI and FTC (Federal Trade commision) @FTC . We will keep working with @FBI@FTC@hitbtc@binance@cz_binance@SlowMist_Team@zachxbt@Google to find the hacker and recover the fund.
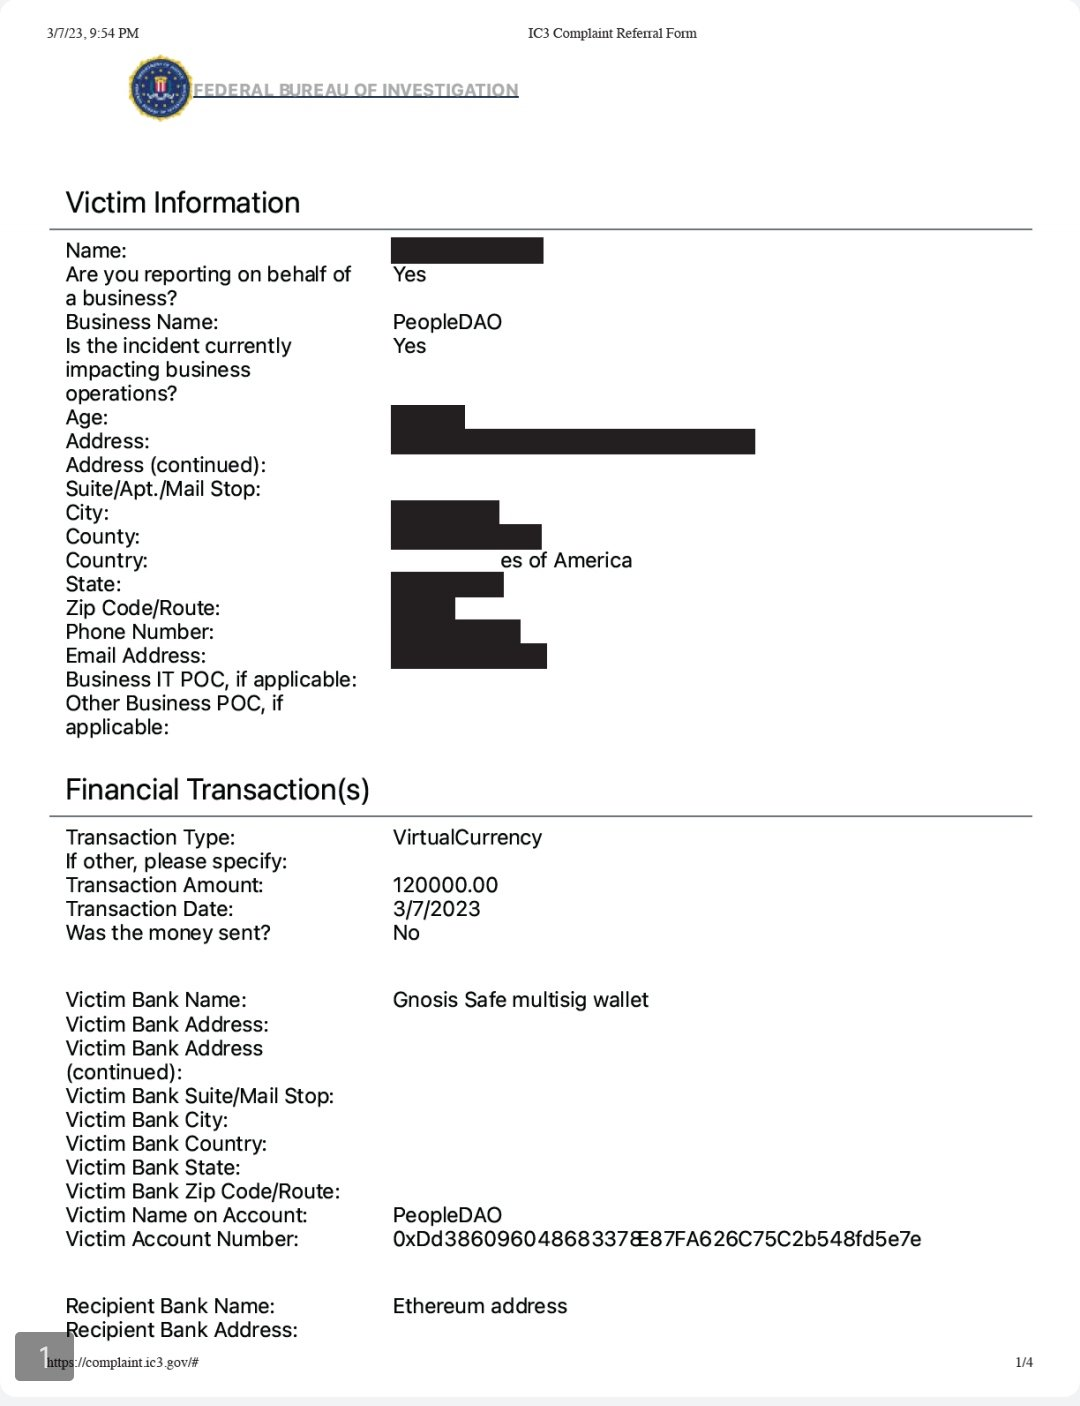
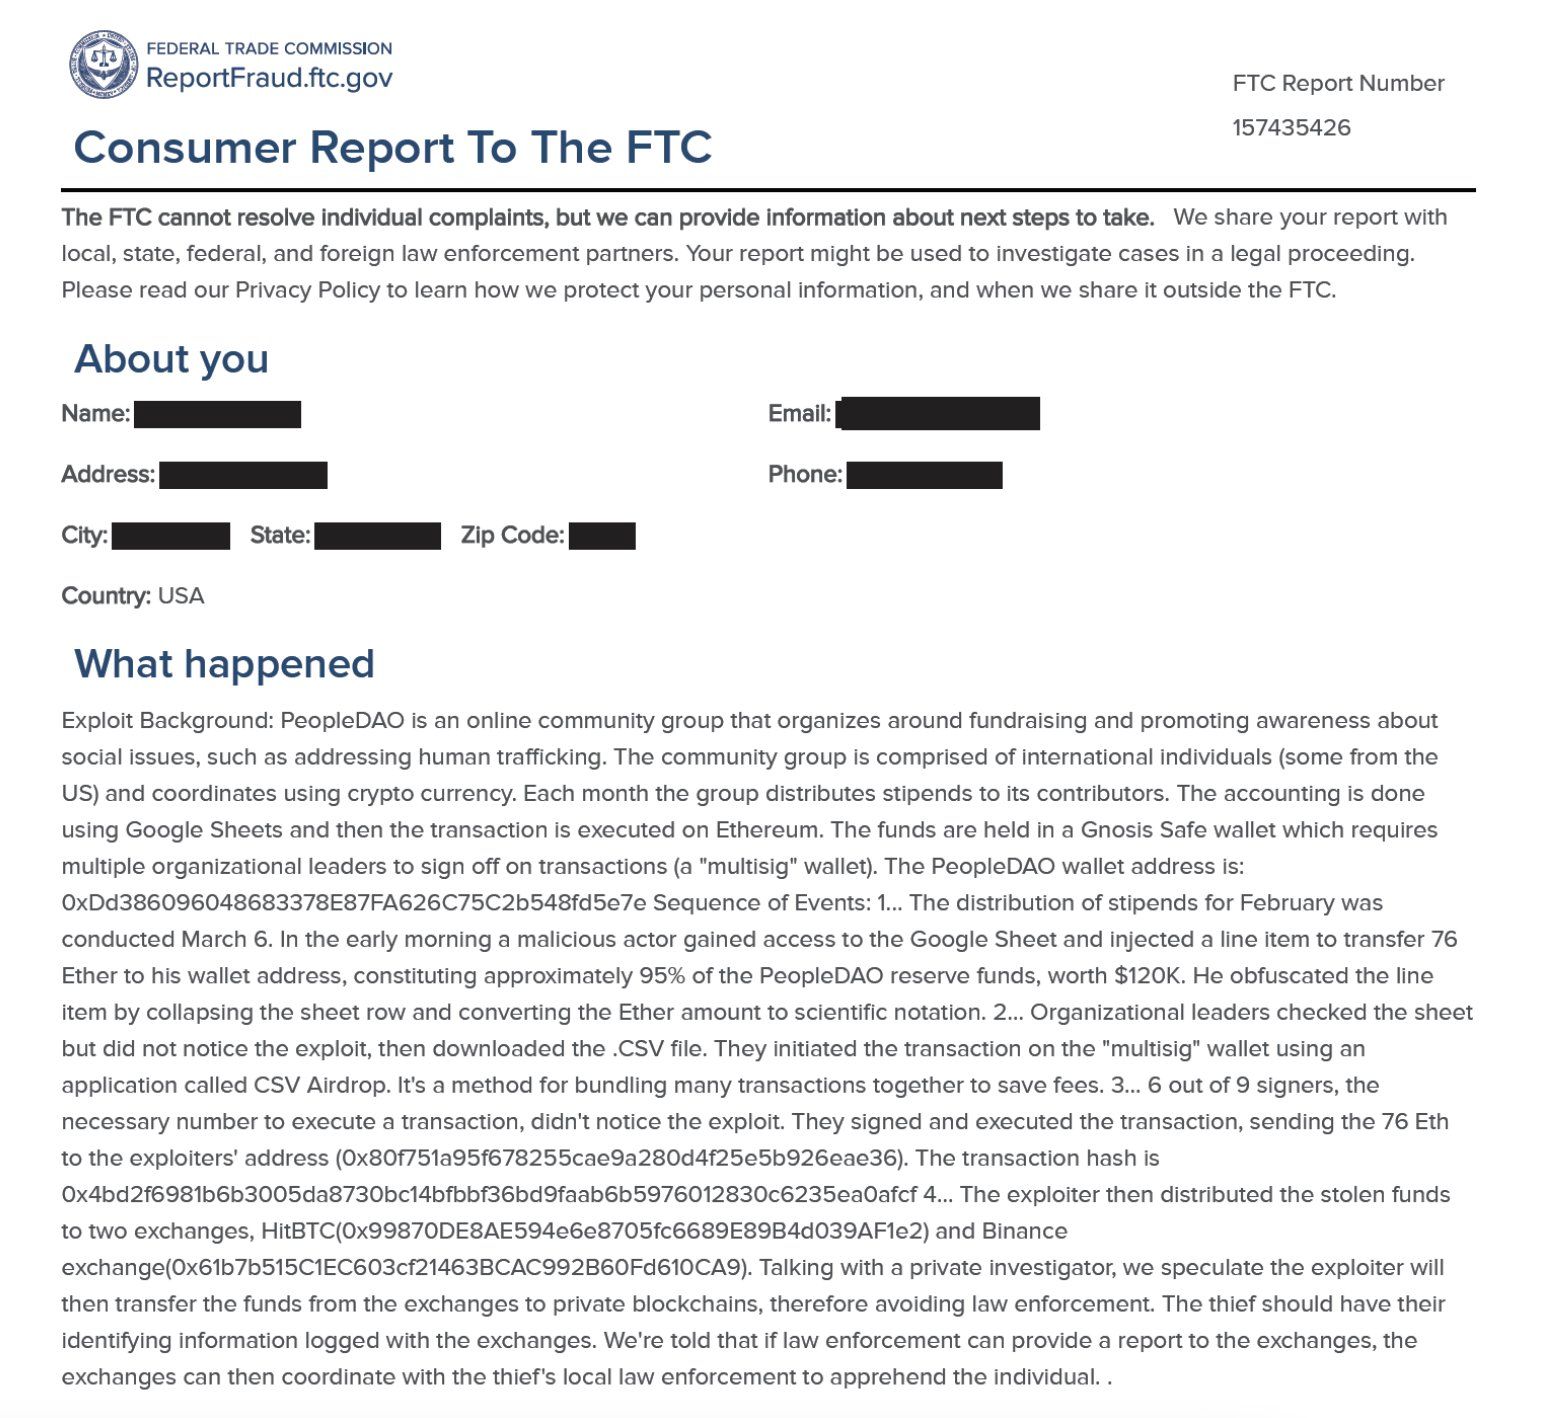
8/10 We offer the hacker a 10% white hat bounty if he/she would return the stolen fund in next 48 hrs.
9/10 The lesson learned: 1. Strictly control the access of the accounting sheet. 2. Multisig signers should check every details before signing. 3. We need a better UI on @safe to show the gross amount of the transaction, such as the total amount of $ETH and $PEOPLE transferred.
10/10 Thanks to the support from community members and contributors, PeopleDAO will operate as usual, building For The People.
We highly recommend other DAOs learn from this case and improve their accounting and treasury management!


All Comments