


On Dec 16, 2022, at 12:12 UTC, a malicious actor began an exploit on the Raydium Liquidity Pool V4’s authority account by gaining access to the Pool Owner (Admin) account.
OtterSec posted an initial overview of the attack.
This update also expands on the initial post-mortem posted on Twitter by Raydium’s official account.
This detailed post-mortem attempts to provide an in-depth description of how the exploit was carried out, how the issue was mitigated, and the next steps.
Background:
The Pool Owner account mentioned above was initially deployed on a virtual machine with a dedicated internal server. After additional review, there is currently no evidence that the private key for the Pool Owner account was ever passed, shared, transferred, or stored locally outside of the virtual machine where it was originally deployed.
An internal security review is ongoing in order to determine the nature and root cause of the account compromise. Initial suspicions are that the attacker may have gained remote access to the virtual machine or internal server where the account was deployed. The exact intrusion vector has yet to be identified, but a trojan attack may be one possibility.
An initial review indicates that the Raydium exploiter account is involved in other nefarious activity on Solana. One indication of this is a tweet from cloudzy.sol on Nov. 7 that details a wallet exploit amounting to 198 SOL that ultimately arrived in the same account that originally funded the primary Raydium exploiter wallet as mentioned in the initial post-mortem tweet.
Exploit Details
The attacker compromised eight constant product liquidity pools on Raydium, totaling approximately ~4.4m USD in funds stolen. Concentrated liquidity pools and RAY staking programs were not affected by the exploit. Any other pool or funds on Raydium were not affected by the exploit.
The below image indicates assets transferred by the attacker during the exploit from affected pools. ‘Base’ token refers to the token on the left side of the token pair, ‘Quote’ refers to the token on the right side of the pair (usually stablecoin or SOL).
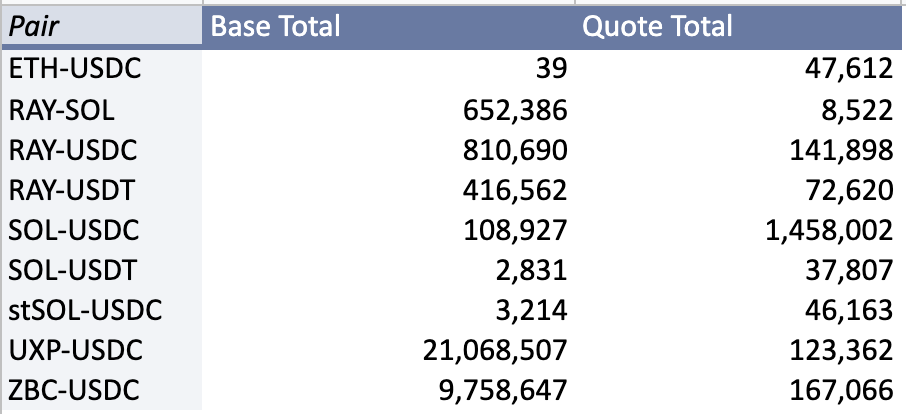
A full list of the transaction history and funds lost can be found here: https://github.com/raydium-io/dec_16_exploit
The exploit happened in two parts:
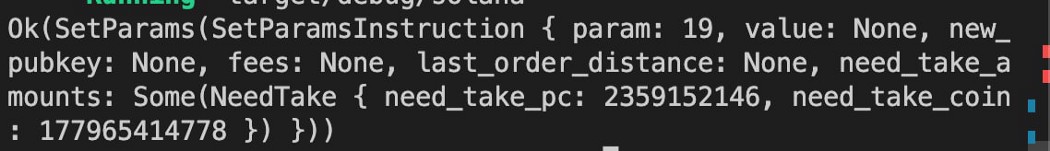
- The withdrawPNL instruction is in place to collect protocol fees for RAY buybacks and is based on a predefined amount of assets determined by need_take_pc and need_take_coin, which should be equivalent to 12% of total fees earned by the pool or 3bps of the 25 bps earned from swap transactions. The attacker used this function to withdraw funds (designated as fees) from the pool vault. After withdrawPNL is initiated, the need_take_pc and need_take_coin calculation automatically resets to zero.
- The attacker used the SetParams instruction in conjunction with AmmParams::SyncNeedTake to inflate the balances for need_take_pc and need_take_coin without trading volume needing to occur, allowing the attacker to alter and increase the expected fees and then withdraw the funds (designated as fees) from the pool vault via withdrawPNL, repeatedly.
Initial Mitigation of Exploit
On Dec 16, 2022 at 14:16 UTC, Raydium deployed a hot patch, or stub, also known as a controllable replacement for an existing dependency for all programs. In other words, the authority of the compromised account (HggGrUeg4ReGvpPMLJMFKV69NTXL1r4wQ9Pk9Ljutwyv) was revoked and was updated to a new account held on a hardware wallet.
This patch revoked the attacker’s authority and ability to further exploit the pools.
Additional Security Steps Taken
Dec 17, 10:27 UTC: The Raydium AMM V4 program was upgraded via Squads multisig to remove unnecessary admin parameters that could potentially have an effect on funds if compromised.
The following parameters were removed:
- AmmParams::MinSize
- AmmParams::SyncLp
- AmmParams::SetLpSupply
- AmmParams::SyncK
- AmmParams::SyncNeedTake
Additionally, all admin parameters were removed for:
- Raydium Stable Pools
- Raydium Acceleraytor
- Raydium DropZone
All remaining admin parameters, including the withdrawPNL function, were updated to the Squads multisig currently used for program upgrades at approx 15:00 UTC on Dec 17.
Next Steps
Raydium is approaching next steps on two fronts, concurrently:
- Accurately determining the impact of the exploit on the pools for user LP balances
Raydium is pulling snapshots and collating data for all LP balances and corresponding position sizes before the hack occurred, as well as extrapolating the discrepancy in original balances that resulted from the exploit. Ensuring that an accurate account of balances is determined is necessary to determine a suitable solution going forward. It will take some time to obtain accurate information for all accounts and LP balances in the affected pools, patience during this time is greatly appreciated.
2. Tracking attacker wallets and exploring options for the return of funds
Raydium has been in contact with a number of Solana teams, 3rd party auditors and centralized exchanges that have provided support and potential leads in regards to the attacker and relevant accounts. While there is nothing definitive at the moment, evidence has emerged connecting the wallets involved (as mentioned in ‘Background’ above) in the exploit to previous NFT rug projects and malicious draining of user wallets. Raydium will continue to communicate with relevant teams and security experts to explore avenues for retrieving funds.
Raydium is offering a 10% bounty in exchange for returning funds. Raydium offers the exploited RAY balance as an additional bounty.
Moving forward
There is still work to do to assess the overall impact to individual user LP balances and funds. While Raydium understands that all parties are anxious about the funds in question, time is still needed to collect data and information before all options for a way forward can be assessed. Additional details will be communicated as they become available.
If you have any relevant information about the attacker or the nature of this exploit, please connect via the Raydium Discord server.


All Comments